Keep access out of your maintenance notes
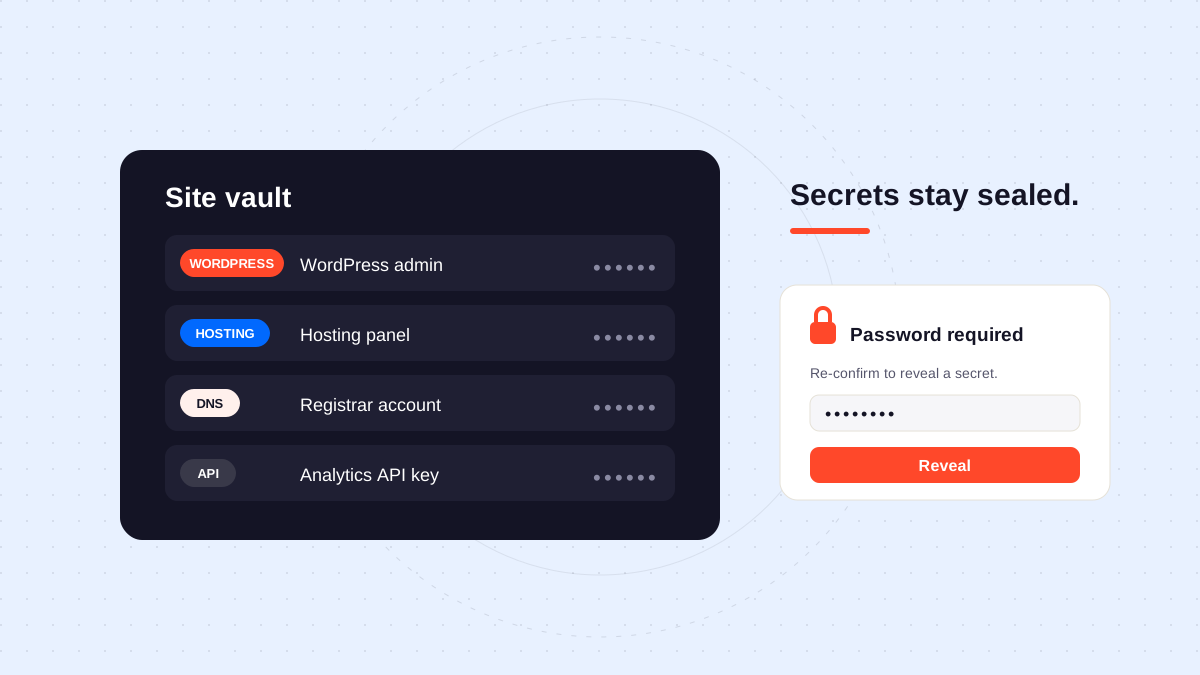
Record who owns an account and where approved access is managed. Store the credential itself in the team's dedicated credential system.
Maintenance notes need to be easy for the right people to find. Credentials need a more deliberate access process. Combining the two makes both jobs harder.
Record the reference, not the secret
A useful website record identifies the service, its account owner, and the approved place to request or retrieve access. Avoid copying passwords, recovery codes, API tokens, or private keys into a checklist.
- Name the service and its role in the website.
- Identify the account owner and maintenance contact.
- Point to the relevant credential-manager entry.
- Explain who can approve a change to access.
Review access during a handover
When responsibility changes, check that the new owner can perform the agreed work. Revisit permissions for previous collaborators through the team’s established access process.
A record that says “ask the developer” becomes less useful when that person is unavailable. Give responsibilities a named owner and keep the record current.
Keep reports appropriate for their audience
Client updates can describe that access was reviewed without revealing the access details. Link to a restricted internal record only when that audience should have access to it.
Explore Orbit’s security page for the product’s access boundaries, and use the handover checklist when maintenance responsibility moves between teams.