01
Tenancy
Each agency is isolated. Sites, members, preferences, contracts, and integrations do not leak across tenants. Operators and viewers only see the sites they are scoped to. Clients see their own site.
Security & trust
Orbit Webmaster is built so the dangerous thing is hard, the recorded thing is default, and the model never gets to skip the queue.
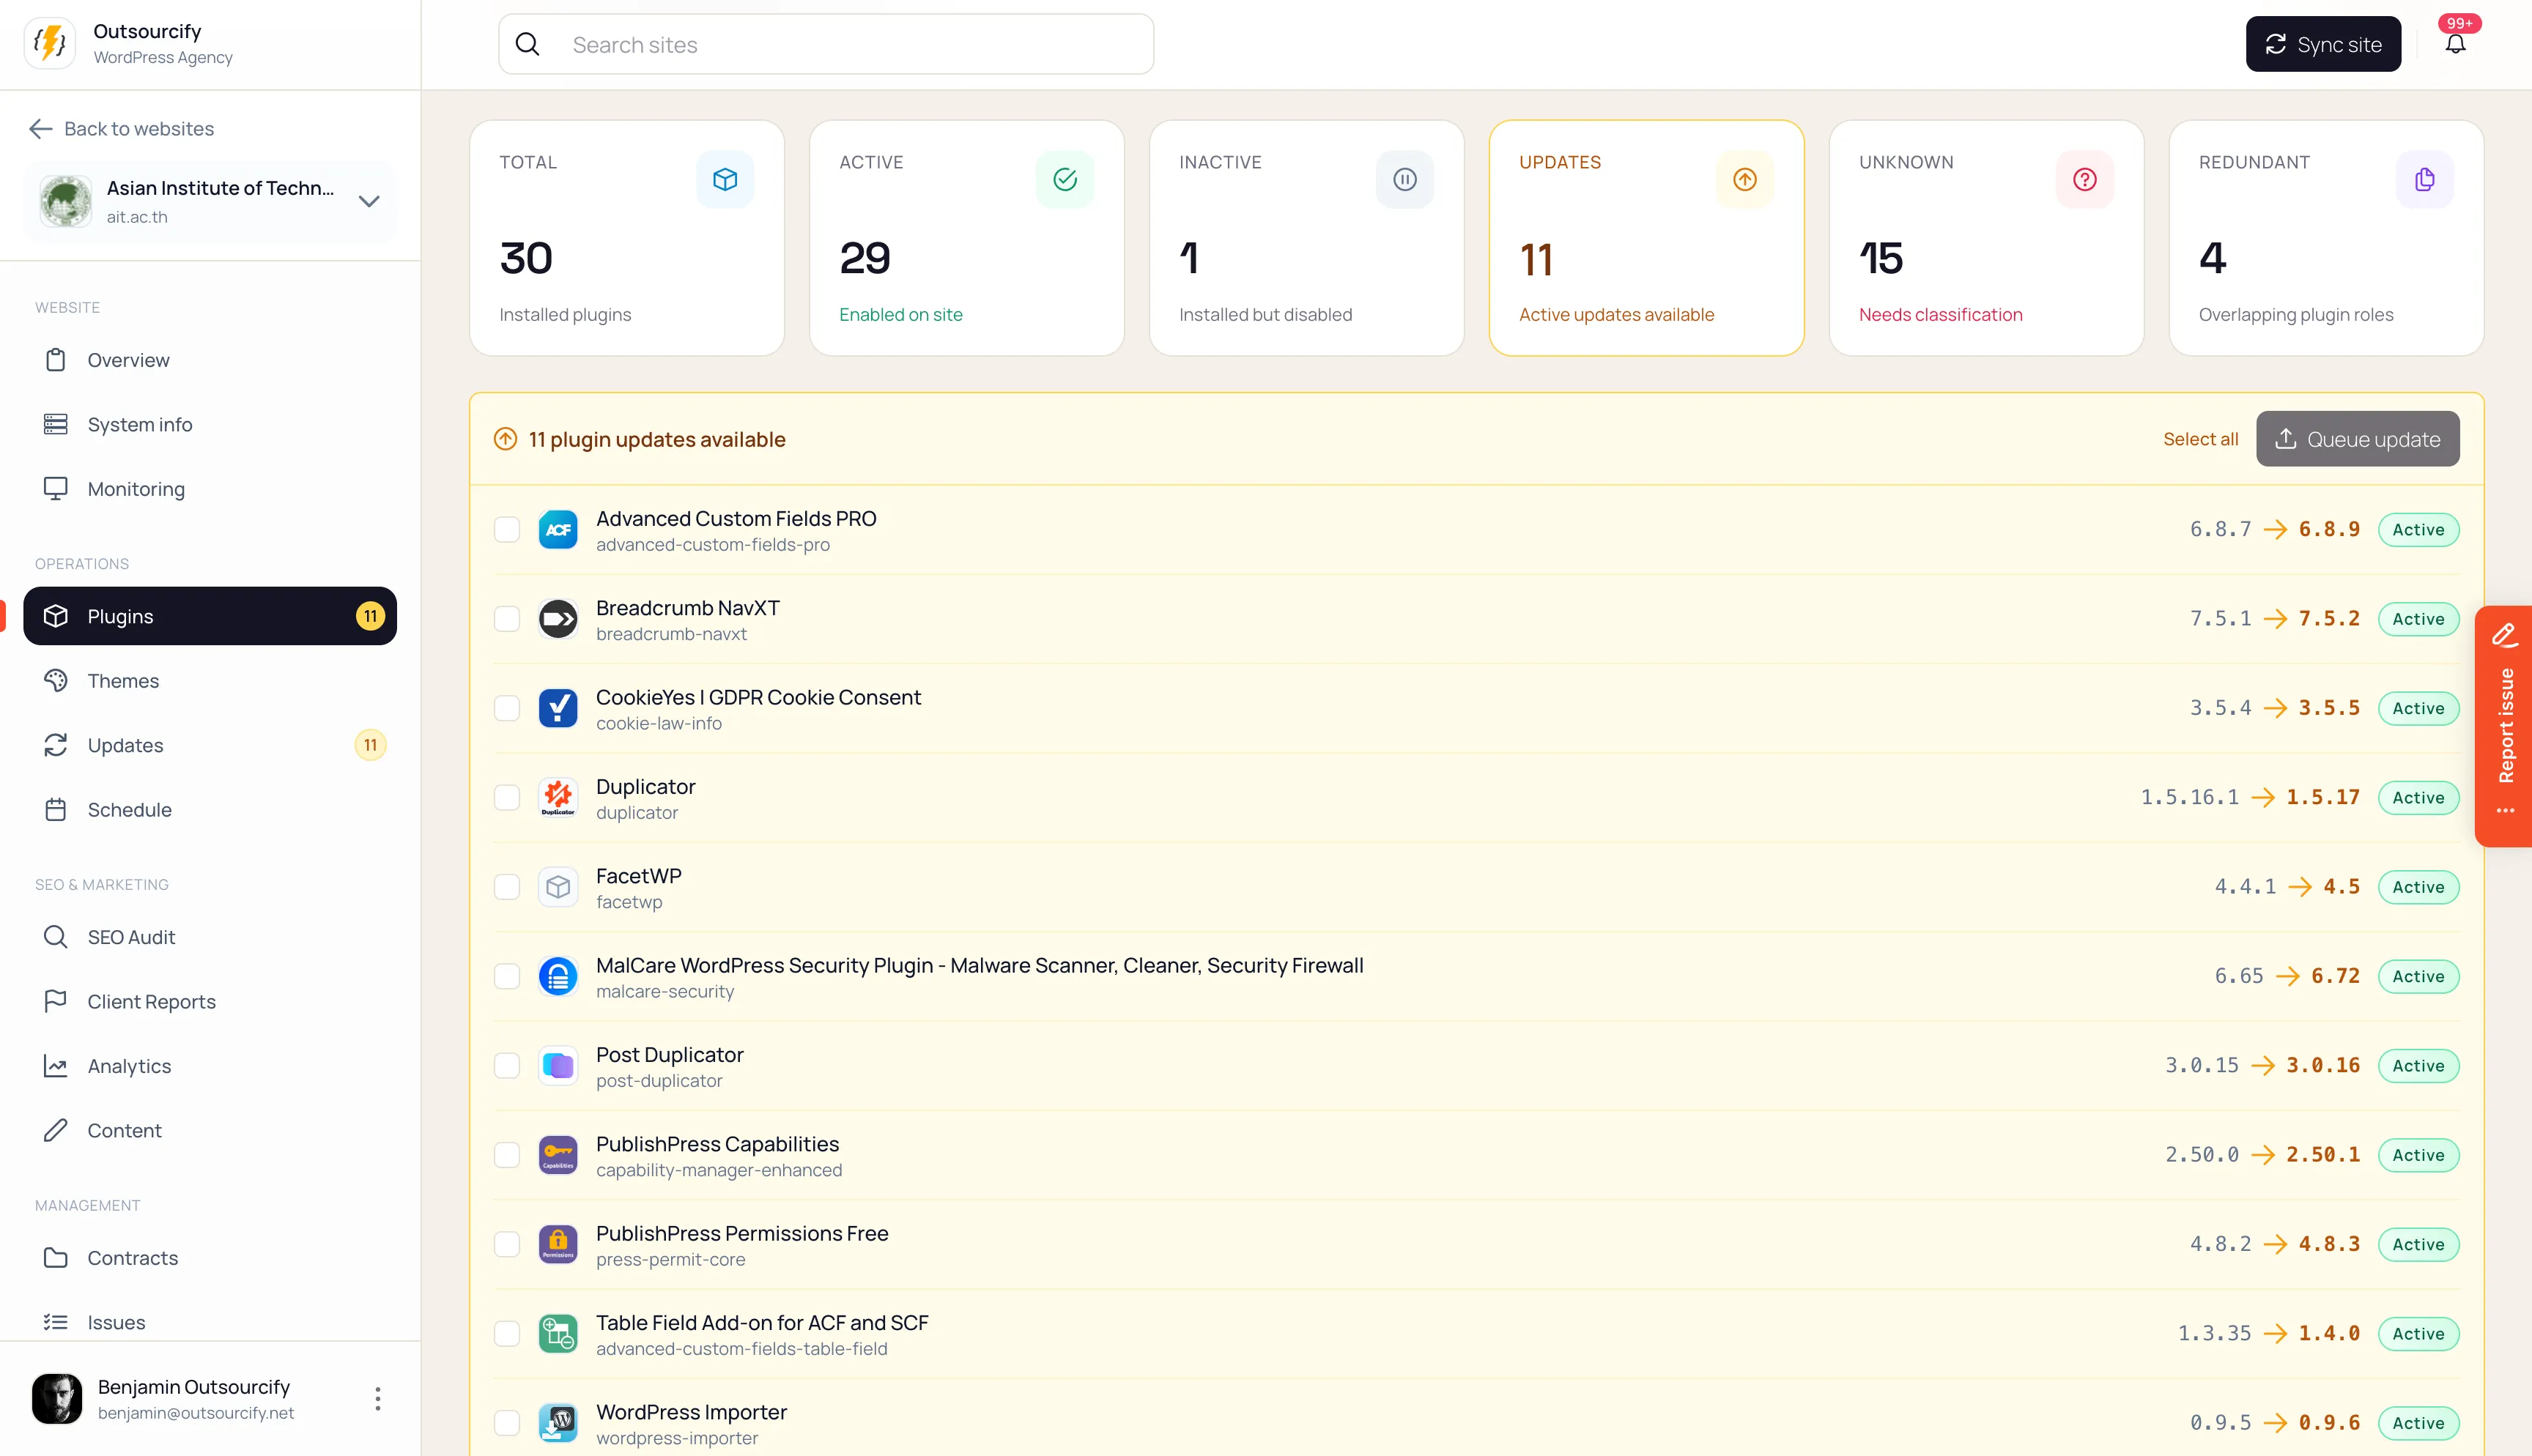
Each agency is isolated. Sites, members, preferences, contracts, and integrations do not leak across tenants. Operators and viewers only see the sites they are scoped to. Clients see their own site.
Per-site connection tokens, hashed and encrypted, rotatable and revocable. The plugin is a thin execution and discovery layer. Business logic, credentials for hosts, and AI all stay on the server.
AI proposes descriptions, classifications, and (later) plans. It does not run actions. Directory changes need a human. Manual site text is never overwritten by a regenerate. When plans exist, they pass schema, permission, capability, and lock checks before anything is queued.
Typed actions. Idempotency. Site locks so two workflows do not mutate the same production at once. Environment locks on deploy. Approval when the action is destructive or the screenshot diff is unclear. History you can query: who planned, who approved, what ran, where, and what came back. Failed tasks do not consume hours.
Updates are modelled as clone → change → look → ship. File rollback on a live site is not a strategy.
GitHub sync uses repository access to read the source of truth and detect drift. It is not a backdoor deploy that skips your existing pipeline.